04Products & Infrastructure
From idea to scalable production system.
We turn ideas into scalable products and run them on infrastructure built for reliability — cloud architecture, delivery pipelines, monitoring, and security from the start.
- 8
- capabilities
- 4
- delivery stages
- 9
- technologies
How we approach it
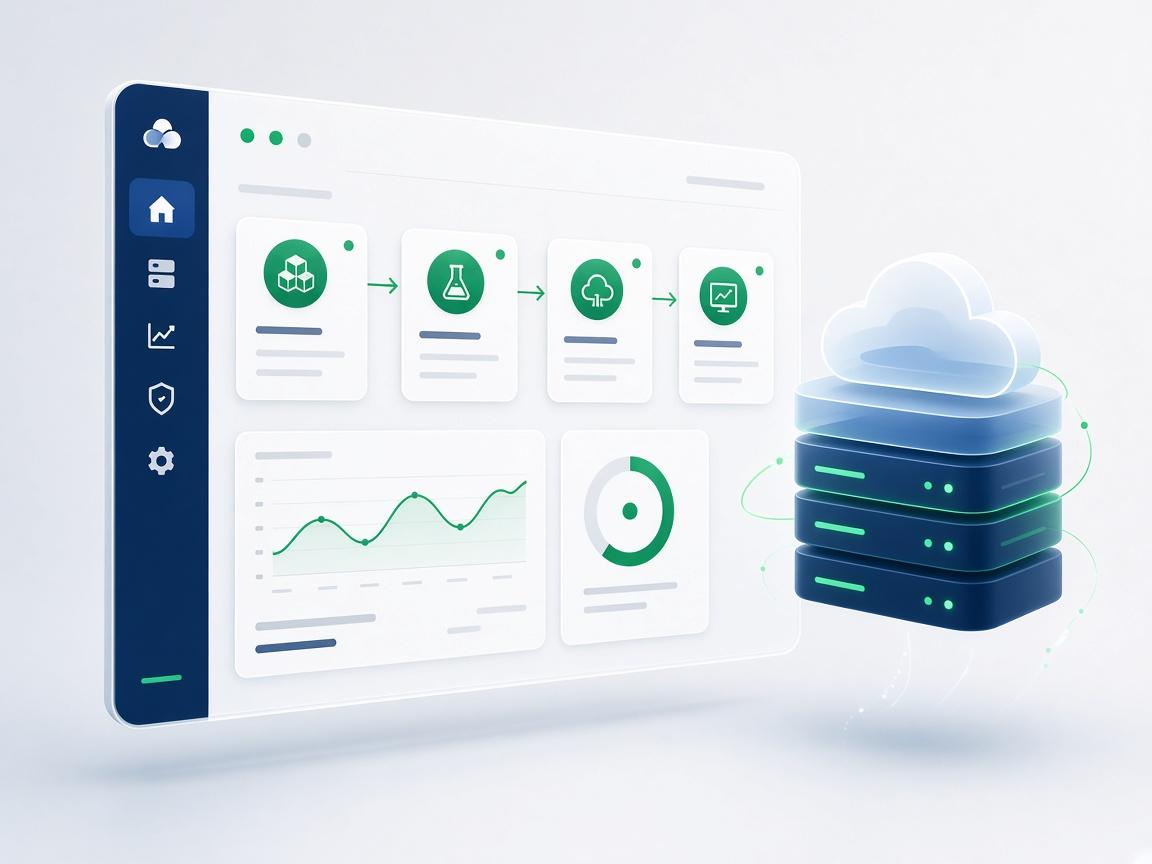
Ship it. Run it. Scale it.
Ship
Move from idea to MVP to production with a delivery pipeline that makes every release repeatable.
Run
Operate with monitoring, alerting, backups, and runbooks, so problems are caught before customers notice.
Scale
Design for growth in users, data, and cost — with the capacity and observability to see it coming.
What we build
Products & Infrastructure, end to end
Eight product and infrastructure capabilities, engineered together so what you launch is what you can operate.
SaaS Product Development
Subscription products with onboarding, billing, roles, and admin tooling designed in.
- Billing & plans
- Onboarding
- Admin console
MVP → Production Engineering
Harden prototypes into products with proper data models, tests, and operations.
- Refactor plan
- Test coverage
- Release process
Multi-Tenant Applications
Isolated, scalable tenancy with per-customer configuration and data separation.
- Tenant isolation
- Per-tenant config
- Usage metering
API-First Products
Public and partner APIs with versioning, auth, rate limits, and developer docs.
- Versioning
- API keys & OAuth
- Developer docs
Cloud Architecture
Well-architected designs on AWS, Azure, or Google Cloud, balanced for cost and resilience.
- Reference architecture
- Cost model
- Disaster recovery
DevOps & CI/CD
Automated build, test, and deploy pipelines with infrastructure as code.
- CI/CD pipelines
- Infrastructure as code
- Environments
Deployment & Monitoring
Safe releases, observability, and alerting that shorten time to detect and recover.
- Logs & metrics
- Alerting
- Rollback
Security & Reliability Engineering
Secure-by-default design with access control, secrets management, and resilience testing.
- Access control
- Secrets management
- Load testing
Built to be operated
One platform, many customers — safely.
Products only scale if they can be run. We design tenancy, environments, and security together, so adding customers and shipping releases stays routine.
- Separate dev, staging, and production with automated promotion
- Tenant isolation and usage metering designed in
- Security and compliance controls part of the pipeline
System flow
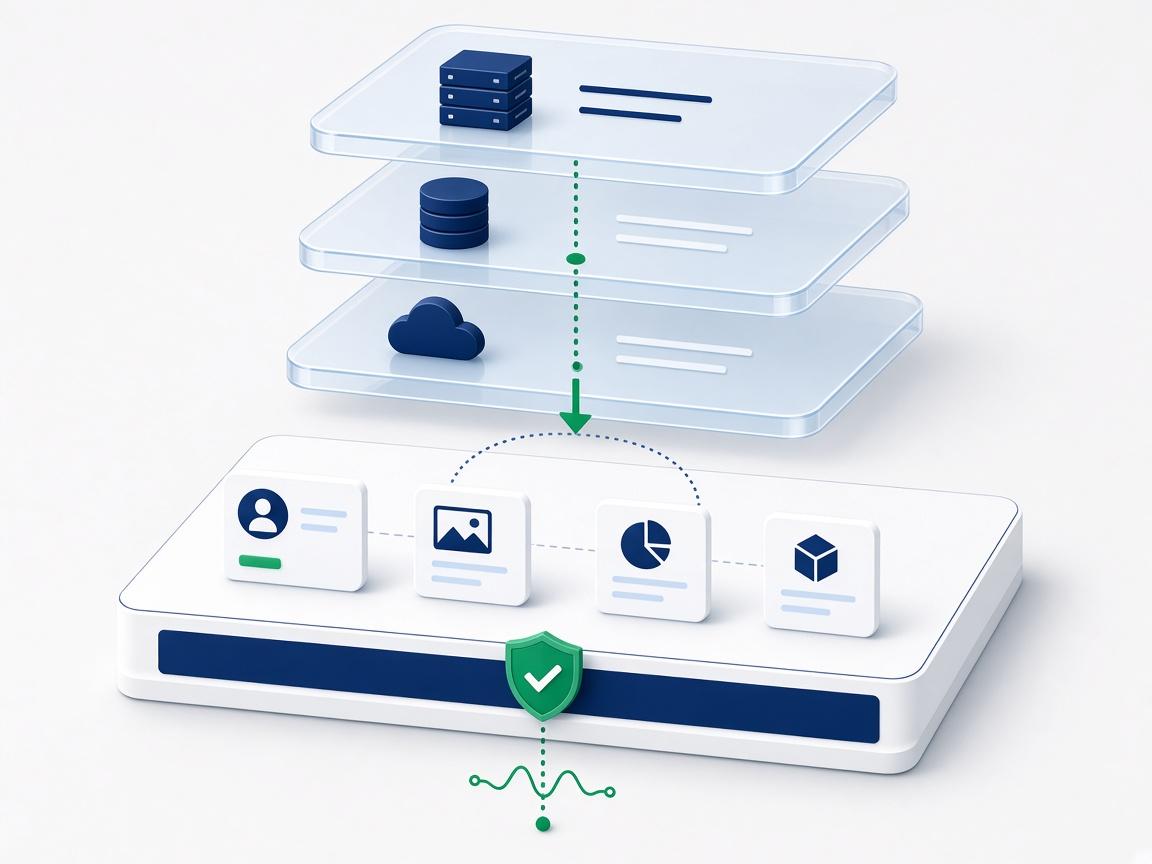
How a release reaches production
Automated gates at every stage — a release only moves forward when it's safe to.
- Product
- Deploy
- Monitor
- Scale
How we deliver
A clear path from first call to production
- 01
Define the product
Clarify users, scope, and the smallest version that proves the idea.
- 02
Design the platform
Choose cloud architecture, tenancy, environments, and the delivery pipeline up front.
- 03
Build & automate
Develop in increments, with infrastructure as code and automated testing from the first commit.
- 04
Operate & scale
Launch with monitoring and runbooks, then tune capacity, cost, and reliability as usage grows.
Technology
Tools and platforms we work with
We choose the simplest technology that fits the problem — and work in your stack where you have one.
AWS
Microsoft Azure
Google Cloud
Docker
Kubernetes
Terraform
GitHub Actions
PostgreSQL
Redis
Engagement outcome
What you receive
- Deployed product running in your cloud account
- Infrastructure as code and CI/CD pipelines
- Monitoring, alerting, and logging dashboards
- Security and disaster-recovery documentation
- Operations runbook and team handover
Where it applies
Industries and solutions
FAQ
Questions we hear most
Straight answers about how we work on this kind of project.
Can you take over infrastructure we already run?
Yes. We start with an audit of what exists — architecture, cost, security, and reliability — and then propose improvements in priority order without disrupting production.
Which cloud platforms do you work on?
AWS, Microsoft Azure, and Google Cloud. We recommend based on your existing footprint, compliance needs, and the services your product depends on.
How do you approach security?
Security is built into design and delivery: least-privilege access, secrets management, dependency scanning in CI, encryption, and logging. We document controls to support your own compliance work.
Can you take a prototype to production?
That's a common engagement. We review the prototype, keep what's sound, replace what isn't, and add the testing, operations, and security needed for real users.
Keep exploring
More of what we do
Ready to start with Products & Infrastructure?
Tell us about the problem. We'll come back with an honest view of the right approach, and what a first increment looks like.